Authentication vs. Authorization: Checking Access to Each Resource
Learn how authentication and authorization differ, where to enforce invoice permissions, and how to test roles, organization boundaries, and denied access.
Learn how authentication and authorization differ, where to enforce invoice permissions, and how to test roles, organization boundaries, and denied access.
Learn how antivirus detects threats, what to do with an alert, how to configure protection, and why a clean scan does not guarantee a file is safe.
Plan backups around recovery time and data loss, protect separate copies, and test restores of projects, databases, and recovery keys.
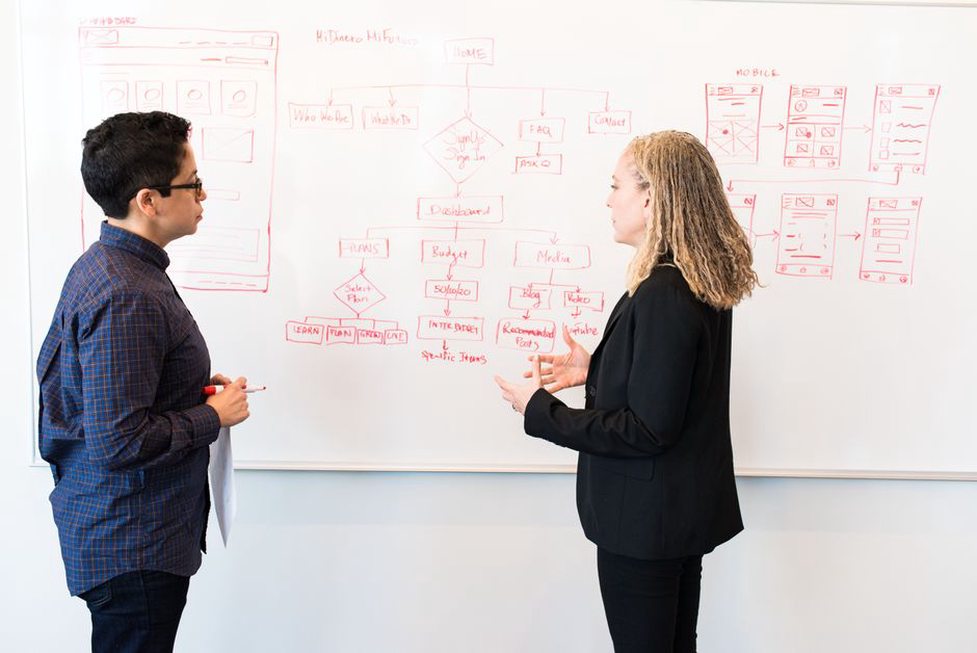
Learn where web applications need authorization, safe input handling, session and CSRF protection, secure configuration, and practical tests in a local notes project.
Practical C++ checks for memory ownership, buffer bounds, size arithmetic, input parsing, error handling, and testing in authorized environments.
Learn why patches matter, how to prioritize updates, and how to confirm fixes are running across operating systems, applications, and development dependencies.
Learn when Java concurrency helps, how to run tasks with an executor, coordinate shared state, handle cancellation, and test for thread problems.
Protect sending credentials, authenticate your domain, design safer account emails, and test reset links and delivery without exposing sensitive data.
Learn to map a small app’s data flows, identify testable threats, prioritize risks, and verify safeguards using an authorized study-planner exercise.
Build security into requirements, design, code review, testing, releases, and maintenance with practical SSDLC habits for small development teams.